Articles
Your Software Is Making Decisions. Do Individuals Know?
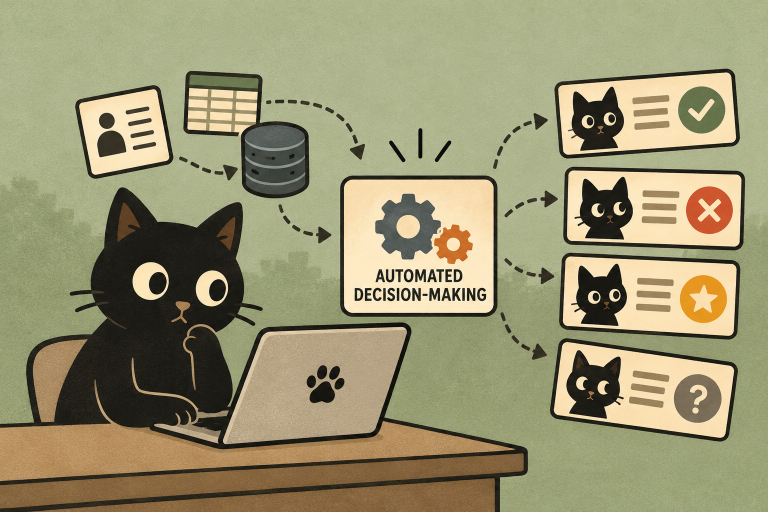
The Office of the Australian Information Commissioner (OAIC) has released new guidance on automated decision-making transparency, which is likely to impact most organisations doing business in Australia. From 10 December 2026, organisations covered by the Australian Privacy Act will have additional obligations to explain certain uses of automated decision-making in their privacy policies / statements.
Privacy by Design Starts Earlier Than You Think
There is a point in most technology projects where someone asks about the privacy risks. The Compliance Notice issued by the Privacy Commissioner to Health New Zealand – Te Whatu Ora following the Manage My Health cyber security breach is a useful reminder of why the timing matters.
Privacy by design isn't about checking privacy at some point during a project, it is about making privacy part of the decisions that shape the project in the first place.
Your Work Email Is Not Your Personal Inbox
Most of us have probably done it at some point. Used our work email address for something that has absolutely nothing to do with work. A recent case from the Office of the Privacy Commissioner is a useful reminder that where personal information is stored can matter just as much as what the information is about.
India's New Privacy Regime is Here but What Does it Mean in ANZ?
India's Digital Personal Data Protection (DPDP) Act, enacted in 2023, is now moving into its implementation phase following the notification of the DPDP Rules in late 2025. The requirements come into force in stages with consent manager provisions commencing in November 2026 and the core operational obligations becoming enforceable from May 2027.
The 13, 13½ or 14 Privacy Principles?
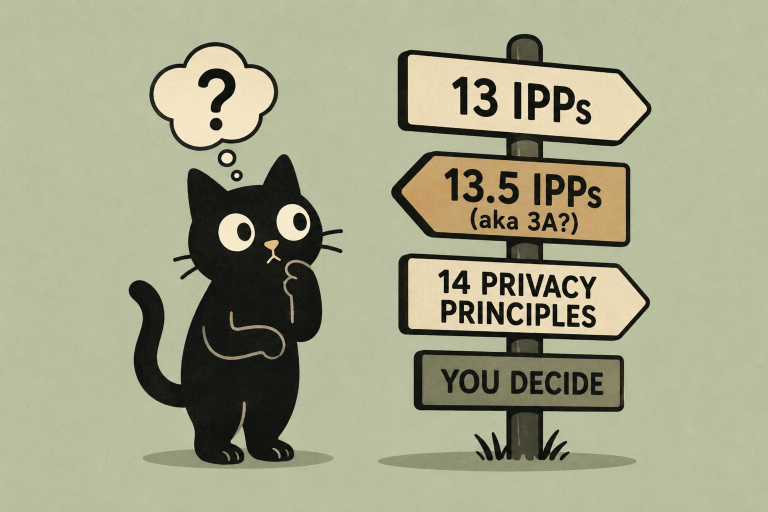
There are few things New Zealand privacy professionals enjoy more than a good academic debate. For years, life was beautifully simple. The Privacy Act had 13 Information Privacy Principles (IPPs). We called them "the 13 IPPs" and everyone knew what we meant.
Then along came IPP 3A.
What Your Website Knows About Your Customers
Tracking pixels have become a standard part of digital marketing, but many organisations don't understand what information they're collecting or where it's going. Here's what the OAIC's latest guidance means for businesses and why privacy should be treated as a business decision, not just a technical one.
Think GDPR Doesn’t Apply? Think Again
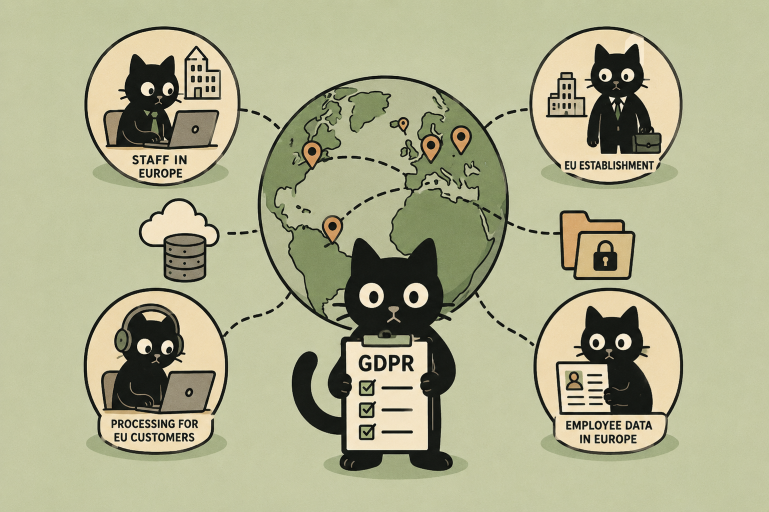
The GDPR was deliberately designed to reach beyond Europe's borders. Whether it applies is not determined solely by where your organisation is located or where your customers are based. Instead, it focuses on the personal information being processed, the people it relates to, and the role your organisation plays in that processing.
When AI Writes the Privacy Act Request
Artificial Intelligence is rapidly changing the way organisations create, store, analyse, and use information. While much of the discussion has focused on productivity, automation, and innovation, another trend is beginning to emerge behind the scenes, a noticeable increase in Privacy Act requests for copies of personal information.
The Myth of “Private” Facebook Groups
Recently a Facebook group that was informal, member-driven, and private became the subject of a legal ruling under the Privacy Act 2020. The case involving the “Bad Tenants, New Zealand (Landlords Only)” group, and the $7,500 award against its administrator for failing to comply with a privacy request.
Your Call is Being Analysed
Cloud Contact Centre as a Service (CCaaS) has become a core part of how organisations in New Zealand interact with customers, bringing together voice, messaging, and digital channels into a single cloud environment. Increasingly, these platforms are powered by artificial intelligence, which promises efficiency and improved customer experience. At the same time, AI introduces a different class of privacy risk, one that is less about simply holding information, and more about continuously analysing, inferring, and reshaping it in ways that are often invisible to the individual.
Controller or Processor: Decide Early
Somewhere between the first line of code and the first paying customer, there is a quiet decision every SaaS builder makes, whether privacy is something you will design, or something you will retrofit. Most choose the latter, not out of neglect, but out of urgency to get to market.
When you build a SaaS product, you are not just creating features. You are defining relationships.
From Conversation to Biometric Data
AI note-takers arrive as something deceptively simple: tools that listen, transcribe, and organize. They promise clarity, efficiency, a kind of external memory that doesn’t tire or drift. But in doing so, they don’t just capture words, they capture voices. A voice is not just data, it can also be biometric information. That distinction matters more than it first appears.
Policies Alone Don’t Provide Protection
During our work we often hear a familiar reassurance: “We have a policy for that.” It sounds comforting and responsible. But a recent decision from the Office of the Privacy Commissioner (PBN3791), involving something as ordinary as a lost USB stick, is a sharp reminder that policies alone don’t protect anything. What is required to mitigate the risk is a combination of controls, readiness, and culture.
Your Phone is Watching the Real You
You probably tell your friends a lot about yourself. Your opinions, your plans, the version of your life that feels safe to share. There’s a kind of control in that, an understanding that what people know about you is, at least partly, your decision.
Your phone however doesn’t work like that. It watches, quietly, constantly, without needing permission in the way we usually think about it. Your phone is watching not just what you say, but what you do.
Dead People, Living Privacy Problems
In both New Zealand and Australia, it is often assumed that privacy ends when life does. The Privacy Acts in New Zealand and Australia are both primarily concerned with information about living individuals. Once a person dies, the rights of access and correction no longer exist along with other obligations under the respective Privacy Act. But stopping the analysis there misses most of what actually matters in practice, individuals.
Your Face is Your Password
In the span of just a few years, the way we authenticate ourselves has undergone a quiet but profound transformation. Passwords, once the cornerstone of digital security, are increasingly being replaced by something far more personal, our faces. From unlocking smartphones to boarding flights and authorising payments, facial recognition has become a seamless part of everyday life.
A Quiet Shift in Privacy Requests
There’s a quiet shift likely to happen with the introduction of IPP3A. Not the kind that arrives with urgency or sweeping change programmes, but something more subtle, something that shows up gradually, in inboxes and workflows, in small moments that start to accumulate. Whereas your organisation used to historically get a scattering of privacy requests this now becomes more frequent. What was once manageable starts to feel persistent. And processes that have quietly worked in the background begin to show their limits.
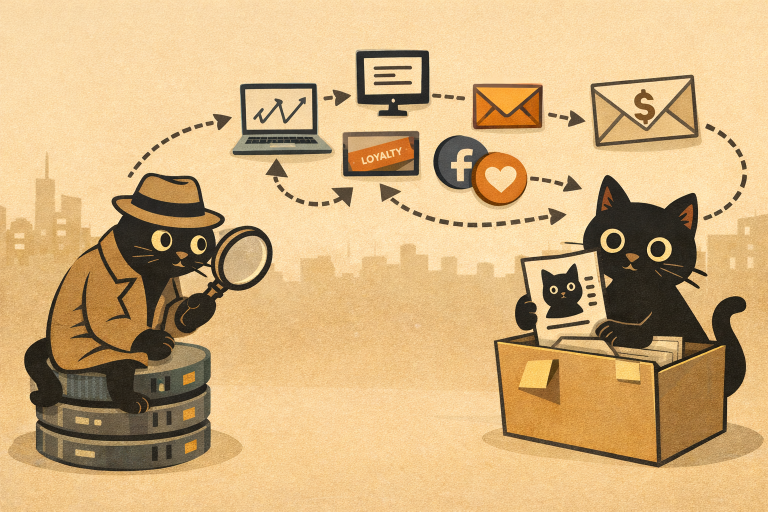
Your Data, Someone Else’s Source
The term data broker often conjures images of shadowy data trading, but the reality is usually much less dramatic. A data broker is simply an organisation that gathers personal information from multiple sources, combines those datasets, and provides the resulting insights to others. From 1 May 2026, changes to the Privacy Act introduce Information Privacy Principle 3A (IPP3A). The amendment strengthens transparency obligations when organisations collect personal information from a source other than the individual concerned.

The Hidden Biometric Systems
The Biometric Code is already in force. But the real deadline for many organisations is still ahead. The Biometric Processing Privacy Code 2025 came into force on 3 November 2025 for any new biometric processing. However, organisations that were already using biometric systems before that date have until 3 August 2026 to comply. Biometric processing is not always visible, sometimes it appears in very ordinary workplace tools.
The Harm Behind Harmless Gossip
We’ve all been there, a quiet aside after a meeting, a message sent with good intentions, a casual “Oh, did you hear about…?” It doesn’t feel like gossip in the moment. Sometimes we tell ourselves we’re helping others be supportive, preparing them to show up for someone who’s going through a hard time. But there is a line, and when it’s crossed, what appears to be innocent sharing can become a privacy breach with very real human consequences.