Articles
Think GDPR Doesn’t Apply? Think Again
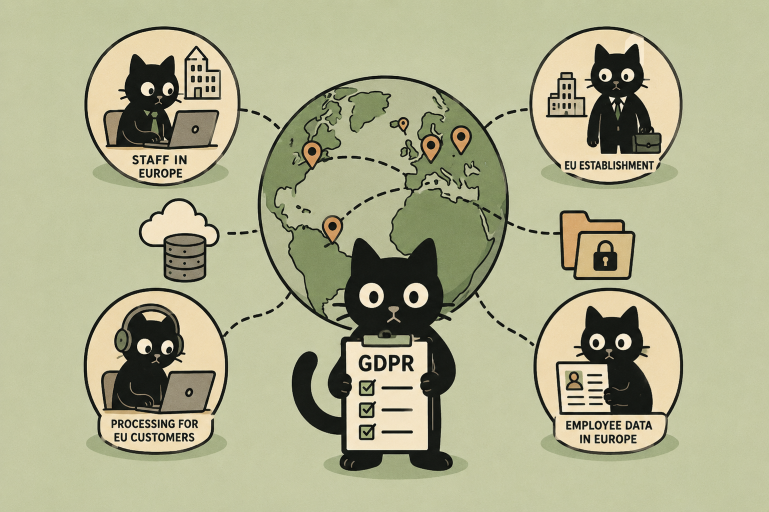
The GDPR was deliberately designed to reach beyond Europe's borders. Whether it applies is not determined solely by where your organisation is located or where your customers are based. Instead, it focuses on the personal information being processed, the people it relates to, and the role your organisation plays in that processing.
Controller or Processor: Decide Early
Somewhere between the first line of code and the first paying customer, there is a quiet decision every SaaS builder makes, whether privacy is something you will design, or something you will retrofit. Most choose the latter, not out of neglect, but out of urgency to get to market.
When you build a SaaS product, you are not just creating features. You are defining relationships.
When does the GDPR actually apply to New Zealand companies?
In conversations with New Zealand organisations about their privacy programme, one theme comes up again and again: “We’re using a processor in Europe, so the GDPR must apply to us.” Simply using an EU-based processor does not mean that GDPR applies unless other conditions are met.
Are They a Controller or a Processor?
Understanding the relationship between the parties is especially important when it comes to indirect collection — that is, receiving personal information from a third party rather than directly from the individual.
Cookies: What the UK’s New DUAA Means for Overseas Businesses
The UK Data (Use and Access) Act — DUAA for short — has passed into law, and it’s set to shake up how websites serving UK residents (including NZ businesses targeting UK audiences) deal with cookies.