Articles
Scaling Privacy Risk Management with Microsoft Tools
For many organisations, the privacy assessment process including Privacy Impact Assessments (PIAs) is recognised as an essential part of managing risk, yet the reality of how it is often carried out tells a different story.
Automating the privacy assessment process does not require new, expensive technology or a complete overhaul of systems. In fact, the building blocks for an effective, automated approach already exist within most organisations.
Are you Gifting Personal Information?
Every day across New Zealand, organisations engage vendors to support their operations. In many cases, these vendors require access to personal information to deliver their services.
But a critical question is not asked often enough “Is this vendor just acting on our instructions, or are they using personal information for their own purposes as well?”
When Good Intentions Meet Hidden Risk
More and more organisations are encouraging their people to contribute beyond their day jobs including joining charity boards, helping professional associations, or volunteering in community roles. It’s a positive trend that builds capability, networks, and a sense of purpose. But there’s a quiet privacy risk that often goes unnoticed.
Are You Collecting Indirectly Without Realising It?
When organisations think about collecting personal information, they often picture the direct kind of collection, when someone fills out a form, subscribes to a service, or makes an online purchase. But there’s another, often less visible way that personal information comes into your organisation’s possession, known as indirect collection.
No, You Can’t Redact That!
The Privacy Act gives people a broad right to access their personal information to provide transparency, accountability, and fairness. The act sets the rules for what you can redact when someone makes a privacy request. You can redact information on a number of grounds including that it would breach another person’s privacy, compromise an investigation, endanger someone’s safety, or reveal privileged legal advice.
Sight It, Don’t Store It
In an age where digital convenience often takes precedence over caution, many organisations across New Zealand routinely collect and store photographic identification as part of customer onboarding processes. The most commonly collected documents are driver licences and passports. It can seem efficient, even responsible, to hold on to a copy “for the record.” Yet what feels like a simple administrative safeguard can in fact create a long-term privacy risk that is difficult to unwind.
Purr-sonal Information: Do Cats Have Privacy Rights?
In New Zealand, cats are everywhere — from beloved companions curled up on sofas to stealthy hunters roaming the bush at night. But as our relationship with animals evolves, an interesting question arises: do cats have privacy rights? And if not, should they?
Employee Privacy Across the Tasman
Privacy law in Australia and New Zealand both aim to protect individuals’ rights over their personal information, but the way each country defines and regulates that information reveals some important differences, especially when it comes to how employee personal information is treated.
The Hidden Privacy Risks of Technology Pilots
Piloting new technology is exciting. It’s a chance to explore innovation, test ideas quickly, and see how emerging tools might transform the way we work. Whether it’s an AI solution, a new analytics platform, or a digital service prototype, pilots feel like safe spaces to experiment. But there’s a growing issue that’s easy to overlook in the rush to innovate: privacy.
Why Proportionality Matters
In an age where cameras are everywhere, from shop ceilings to street corners, the question isn’t whether we can watch, but whether we should and to what extent.
Privacy is Not Just Security
The terms privacy and security are often spoken in the same breath, sometimes even as if they mean the same thing. Yet while they are deeply connected, they are not identical. Understanding the distinction between them is essential for any organisation that handles personal information in today’s digital environment.
Privacy Breach vs Breach of the Privacy Act
When something goes wrong with personal information two phrases get tossed around a lot: privacy breach and breach of the Privacy Act. They sound similar, and they often get blurred together in day-to-day conversations. But they mean very different things and confusing them can lead to the wrong response by an organisation.
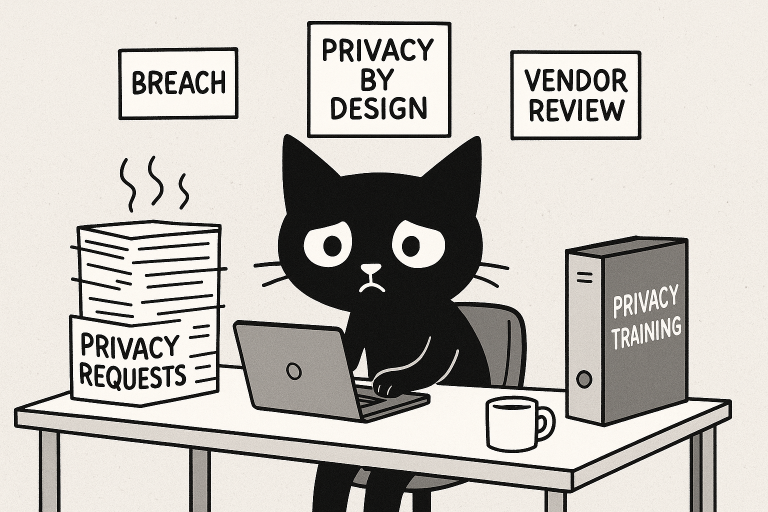
The Loneliness of Being the Only Privacy Person
In many organisations, the responsibility for privacy rests with just one person. That single privacy person is expected to be the responder to breaches, the handler of privacy requests, the privacy by design specialist, the reviewer of vendor arrangements and the trainer of staff, all at once. It’s a role that sits at the heart of trust and compliance, but it is also one that can feel incredibly lonely.
When Machines Decide
Australia has introduced new transparency rules for organisations that rely on these Automated Decision Making (ADM) technologies. From 10 December 2026, the Privacy Act will require organisations to explain their use of ADM when those decisions significantly affect the rights and interests of an individual.
When Police Come Knocking
It’s a scenario that makes many organisations pause: the police call, email or turn up asking for personal information. There’s a strong instinct to help, however, there’s the requirement to protect the privacy of the people whose information you hold.
IPP 3A Clears Third Reading: The Time to Act is Now
Last week Parliament passed the Privacy Amendment Bill through its third reading, confirming the introduction of a new Information Privacy Principle IPP 3A focused on indirect collection. This isn’t a change that can be left until the week before commencement. The work must start now.
The Privacy Act: No Free Pass for Charities and Societies
When most people think about the Privacy Act 2020, they picture government agencies, and big corporates. But here’s the truth: it applies just as much to your local sports club, a neighbourhood charity, or a professional society as it does to corporates. Being a not-for-profit doesn’t mean you’re exempt.
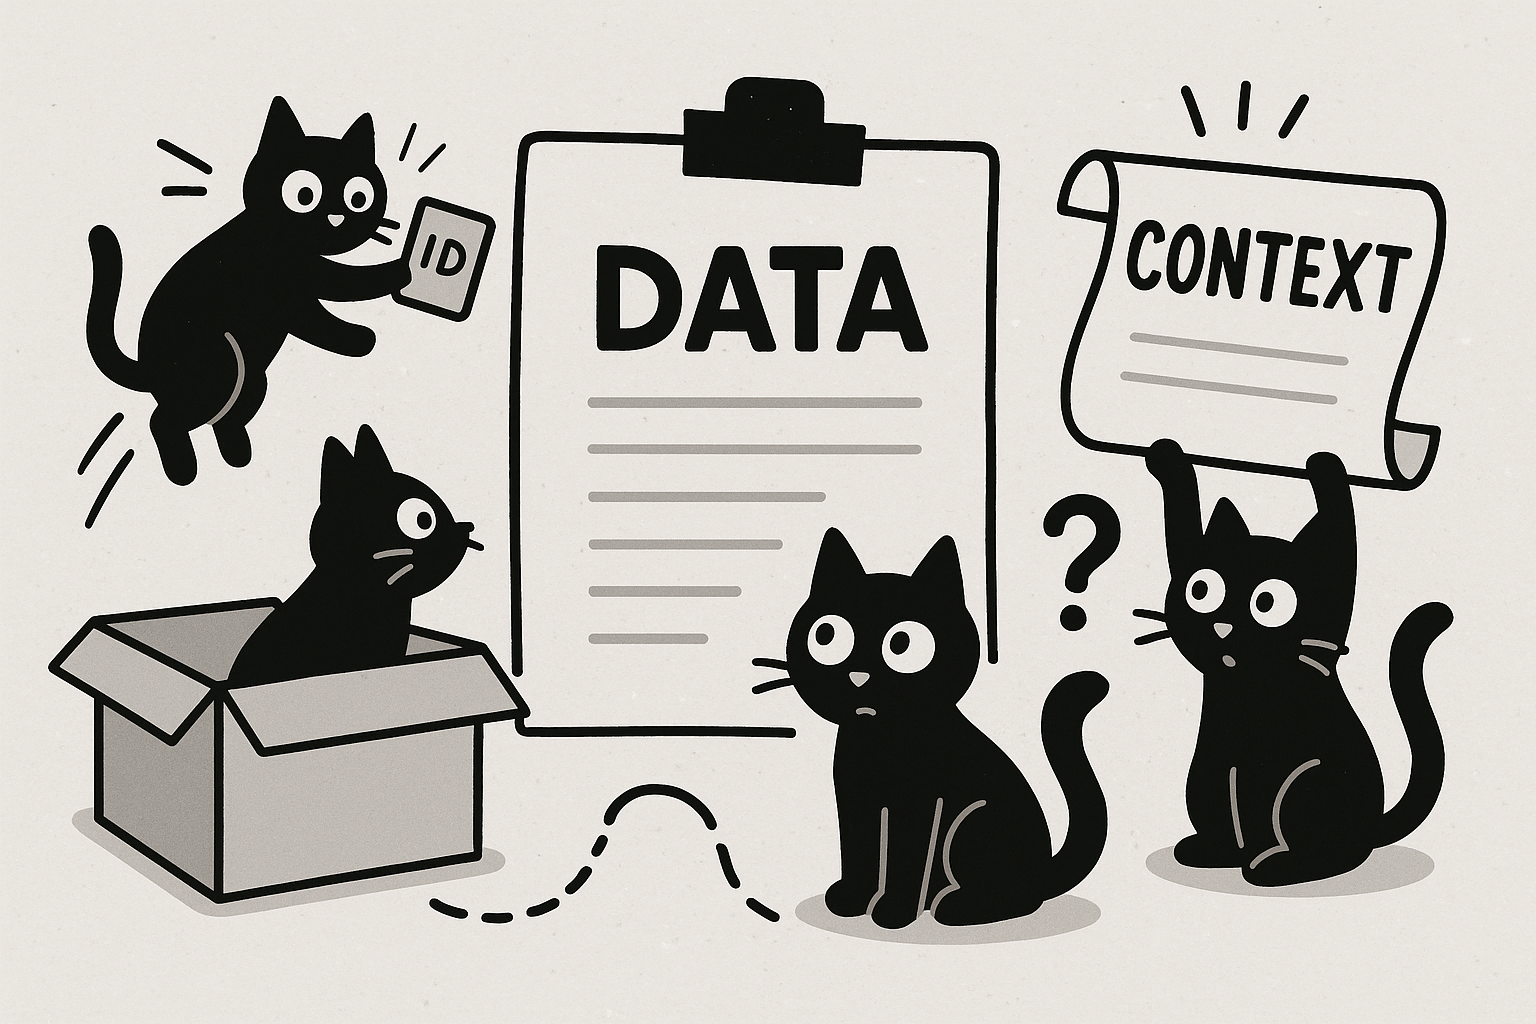
The Pitfall of Cataloguing Without Context
In the rush to show progress on privacy, many organisations begin by building data catalogues of personal information. They invest in tools, run workshops, and inventory every system, every database, every field. On the surface, this feels like progress: “we’ve mapped our personal information.” But the truth is, without context, cataloguing is a dead end.
When does the GDPR actually apply to New Zealand companies?
In conversations with New Zealand organisations about their privacy programme, one theme comes up again and again: “We’re using a processor in Europe, so the GDPR must apply to us.” Simply using an EU-based processor does not mean that GDPR applies unless other conditions are met.
Privacy Policy vs. Privacy Statement - Why the Difference Matters in NZ
Scroll through many organisations’ websites in New Zealand and you’ll find a link to something called a “Privacy Policy.” Nine times out of ten, though the content isn’t a policy at all it’s a privacy statement. And while the difference might seem like splitting hairs, in practice it reveals a lot about how seriously an organisation takes privacy and the level of privacy maturity.